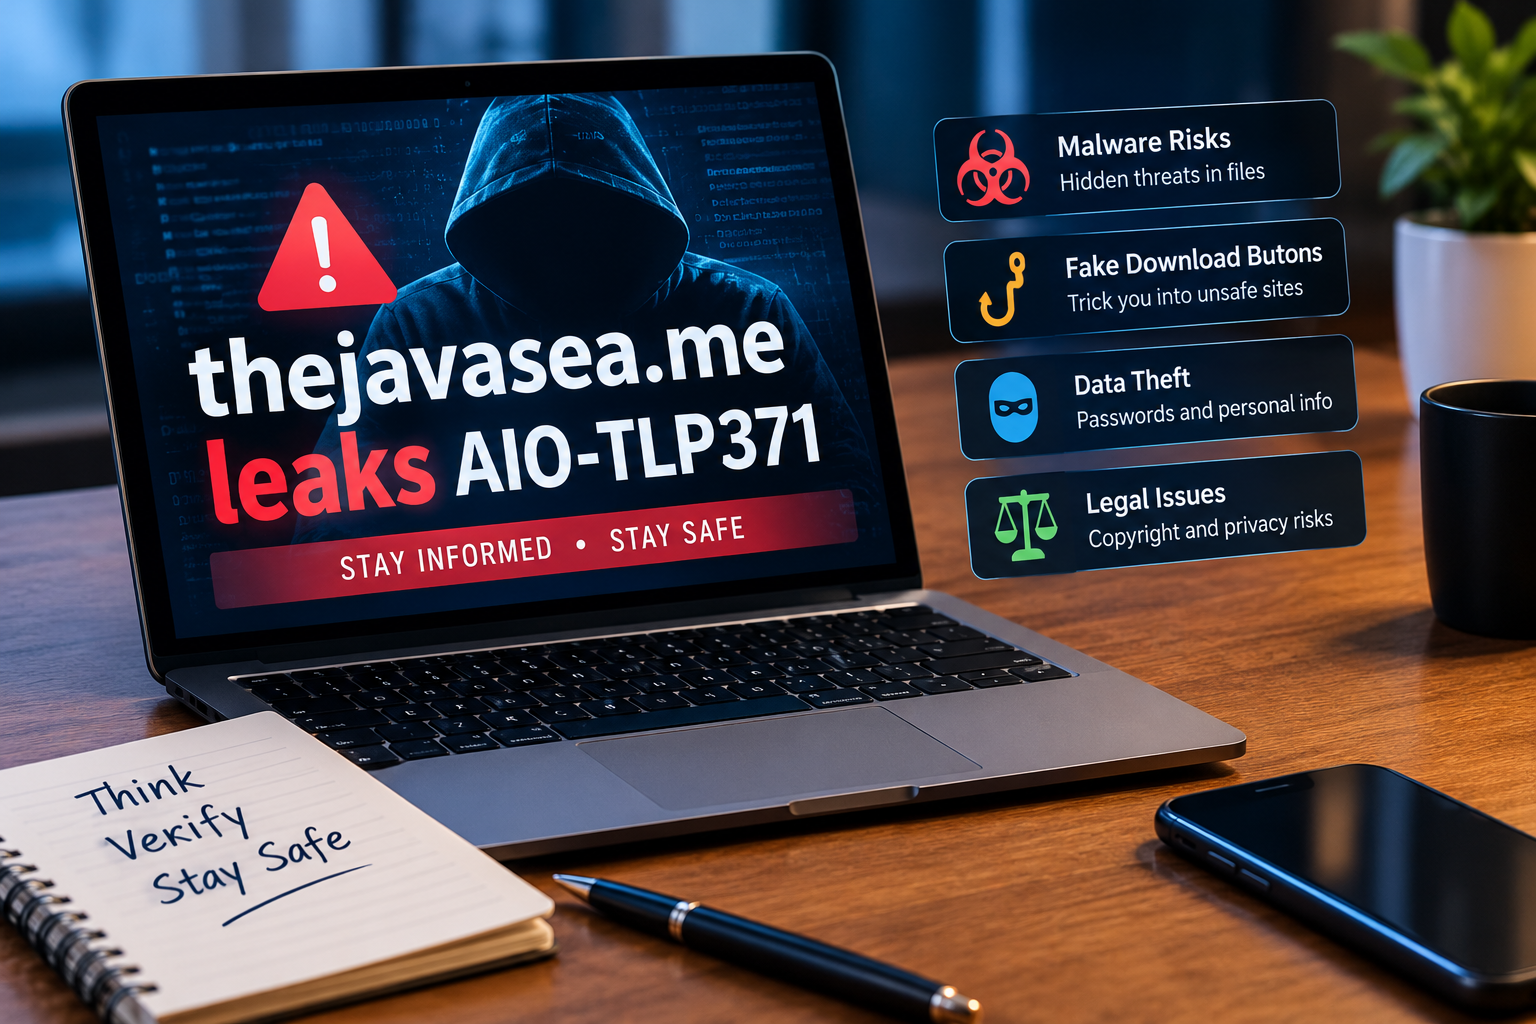
What Is theJavaSea.me Leaks AIO-TLP371?
The phrase thejavasea.me leaks aio-tlp371 appears to be a search term associated with a website, alleged leaked material, and a label called “AIO-TLP371.” Without reliable verification of the specific files or claims behind this label, it is not possible to confirm exactly what the package contains or whether the material is authentic. Understanding the potential security, privacy, and legal risks can help people make safer decisions when they encounter such searches online.
Interest in leak-related keywords often grows when users see discussions on forums, social media, or search engines. Some people want to understand a trending topic, while others may be trying to identify a file or determine whether a website is trustworthy. These are reasonable questions, but unfamiliar names and popular search phrases should not be treated as proof that a file is legitimate or safe.
This guide explains the term cautiously, outlines common risks associated with unverified leak websites, and describes safer ways to protect your information.
Table of Contents
Why Is theJavaSea.me Leaks AIO-TLP371 Trending?
There are several reasons why a phrase such as this may attract attention. However, search popularity alone does not establish that a leak is real, that a file exists in the form described, or that a website is trustworthy.
1. Curiosity about unfamiliar file names
The label “AIO-TLP371” looks like a technical identifier. Labels of this kind can be used for software bundles, archives, online posts, internal project names, or collections of files. Without a trustworthy source explaining this particular identifier, its meaning remains uncertain.
That uncertainty is important. A filename can be designed to sound official even when the contents have nothing to do with the description. Cybercriminals sometimes use recognizable keywords and mysterious labels to make questionable downloads appear interesting.
If you encounter AIO-TLP371 in a forum post or search result, avoid assuming that it identifies a verified product or a confirmed data breach. Look for reliable reporting or an official statement before accepting claims about it.
2. Discussions on forums and social media
Online communities can spread unfamiliar keywords quickly. One person might ask about a supposed leak, another might repeat the claim, and several additional posts may appear without providing independent evidence.
This can create the impression that a topic has been confirmed when the available information is simply being repeated.
A useful approach is to distinguish between three things:
- A search trend: People are looking for information about a term.
- An allegation: Someone claims that files or information have been leaked.
- A verified incident: Reliable evidence supports the claim and establishes what happened.
These categories are not interchangeable. A responsible reader should look for evidence of the third category before drawing conclusions about the first two.
3. Interest in bundled files
The abbreviation “AIO” is commonly used to mean “all-in-one,” although that does not establish what AIO-TLP371 means in this specific context.
All-in-one bundles can sound convenient because they suggest that multiple resources have been collected into a single package. Unfortunately, the same presentation can be used to attract people to unverified archives, deceptive advertisements, or potentially harmful downloads.
The name of a package does not tell you whether it contains the advertised material, whether the files have been modified, or whether running them could put your device at risk.
4. Search engine suggestions and repeated mentions
When users search for a phrase, related suggestions and copied posts can increase its visibility. Websites may also create pages around emerging keywords to attract visitors.
That visibility does not amount to a security assessment. A page can be well optimized for search engines and still provide inaccurate information, misleading claims, or unsafe content.
The key point: treat thejavasea.me leaks aio-tlp371 as an unverified topic unless credible evidence establishes exactly what it refers to.
Is theJavaSea.me Safe or Legit?
The question “is thejavasea.me safe?” cannot be answered reliably from the domain name or keyword alone. A proper assessment would require current technical checks, trustworthy information about the operator, and evidence about the specific page or file being discussed.
It is also important to distinguish between a website being accessible and a website being safe. A page may load normally while still using deceptive advertisements, collecting unnecessary information, or directing visitors toward risky files.
Signs that deserve caution
When evaluating an unfamiliar website, look for the following warning signs:
- It promises confidential, leaked, or exclusive files but provides no credible explanation of their origin.
- It uses repeated pop-ups, misleading download buttons, or unexpected redirects.
- It asks you to disable antivirus software or other security protections.
- It requests browser notifications without a clear reason.
- It requires an unfamiliar extension, executable, or installer to view ordinary content.
- It asks for passwords, payment details, identity documents, or account credentials that are unrelated to the stated purpose.
- It makes dramatic claims but offers no independent evidence.
- It has no clear information about its operator, privacy practices, or contact details.
One warning sign does not automatically prove that a site is malicious. Nevertheless, several of these signs together should make you more cautious.
Does HTTPS mean a website is safe?
No. HTTPS encrypts the connection between your browser and a website, helping protect information while it travels between them. It does not prove that the website operator is honest, that a file is harmless, or that the content is legally distributed.
Fraudulent websites can use HTTPS too. The padlock icon is therefore only one small part of a broader security assessment.
Can you trust user comments and reviews?
User feedback may provide useful clues, but it is not conclusive. Comments can be fabricated, copied, sponsored, or written by people who have not examined a file properly.
A claim such as “I downloaded it and nothing happened” is particularly weak evidence. Some harmful programs operate quietly, steal browser sessions, or wait before carrying out suspicious activity.
Likewise, a positive review does not establish that every file on a website is safe. Assess the source, the specific content, and the available evidence separately.
How should you verify a security claim?
For a suspected data leak, look for reputable cybersecurity reporting, official statements from the affected organization, or notices from recognized security authorities. For a suspicious file, use security tools from reputable providers rather than relying on a stranger’s assurance.
If the claim concerns personal information, avoid sharing the alleged files publicly. They may contain private records belonging to people who never consented to their distribution.
What Are the Risks of Leak and Download Websites?
Not every website discussing a leak is malicious, and not every archive contains malware. Still, downloading files from unverified sources can introduce several kinds of risk.
Understanding these risks helps you make informed decisions without assuming that every unfamiliar website behaves in the same way.
1. Malware hidden inside files
One of the most significant concerns is malware disguised as a document, archive, application, or media file.
A download might appear to be a collection of ordinary resources while actually containing a harmful executable or a document designed to exploit a software vulnerability. Some files may also encourage users to install additional programs before they can view the advertised content.
Potential consequences include:
- Unauthorized access to personal files.
- Theft of saved passwords or authentication information.
- Installation of unwanted applications.
- Monitoring of user activity.
- Disruption of device operations.
- Unauthorized use of the device or its computing resources.
The risk depends on the file, the device, its software, and the actions taken by the user. A filename or file extension alone cannot establish that an item is safe.
Safer practice: Do not open unexpected downloads or run unknown installers simply because a webpage describes them as verified.
2. Fake download buttons and deceptive redirects
Some download pages display multiple buttons that look similar. Only one may correspond to the advertised action, while others lead to advertisements, unrelated websites, or suspicious installers.
A visitor may click a prominent button expecting a document and end up on a page that asks for browser permissions, account information, or another download.
Deceptive pages may also imitate system notifications, security warnings, or familiar software brands to encourage quick decisions.
Be particularly careful with messages claiming that your device is infected and that you must immediately install a particular tool. Genuine security warnings should be checked through the security software or operating system itself, rather than through a random webpage.
3. Password and account theft
A malicious website may attempt to collect login credentials through a fake sign-in form. The page might resemble an email provider, social network, cloud storage service, or another familiar platform.
If you enter a password, the operator may try to use it to access your account. Reusing the same password across multiple services can make the consequences worse.
For example, someone who obtains a password used for an entertainment account might test that same password against email or shopping accounts.
To reduce this risk:
- Use a unique password for every important account.
- Store passwords in a reputable password manager.
- Enable multifactor authentication where available.
- Check the domain carefully before signing in.
- Never provide your email password to a third-party download page without a legitimate, verified reason.
If you entered a password on a suspicious website, change it through the official service. If you reused it elsewhere, update those accounts too.
4. Session theft and browser compromise
Some threats focus on browser sessions rather than passwords alone. A stolen session token may allow an attacker to access an account without entering the password in the usual way.
This is one reason why downloading suspicious browser extensions or running unknown programs can be dangerous. Certain malicious tools attempt to access browser data, stored sessions, or other sensitive information.
If you suspect that an account session has been compromised, sign out of other sessions using the official account settings, change your password, and review recent security activity.
For work accounts, financial services, or accounts containing sensitive information, follow the provider’s incident-response guidance as well.
5. Privacy violations involving leaked data
The word “leak” can refer to many kinds of information, including private messages, personal records, photographs, business documents, or account details. The authenticity and origin of any alleged material must be established before claims about it can be trusted.
Even viewing or sharing leaked personal data can create privacy concerns. Reposting private information may expose victims to harassment, fraud, impersonation, or further unauthorized distribution.
A safer response is to avoid redistributing the material. If you believe the files contain personal information, report the issue through the relevant platform or affected organization’s official channels.
6. Tracking and unwanted browser permissions
Unfamiliar websites may attempt to collect information about browsing behavior or persuade users to enable notifications.
Some notification prompts are legitimate, but a random file-sharing page rarely needs permission to send persistent alerts to your device. Once enabled, unwanted notifications can advertise questionable products or direct you to deceptive websites.
Grant permissions selectively. If you have already allowed notifications and they become intrusive, remove the permission through your browser’s site settings.
7. Financial scams and unexpected charges
A website may advertise free access but later request payment, subscription enrollment, or card details. In some cases, the promised content is never delivered.
Be cautious when a page requests payment through an unfamiliar service, pressures you to act immediately, or hides the total cost behind confusing terms.
Never provide financial details merely to prove that you are a real visitor. If you have already entered card information on a suspicious page, contact your financial institution through its official app or telephone number and ask whether additional precautions are appropriate.
8. Legal and copyright concerns
Leaked material may be protected by copyright, confidentiality obligations, privacy laws, or other legal restrictions. The rules vary by country and depend on the type of material, how it was obtained, and what someone does with it.
Downloading, possessing, distributing, or republishing certain material may create legal risks. Unauthorized disclosure of personal data can also harm the people involved, regardless of whether the files are technically accessible online.
This does not mean every discussion of a leak is unlawful. Reporting on a suspected incident, discussing cybersecurity risks, and accessing lawfully published information are different from distributing stolen or copyrighted files.
When the source or legal status is unclear, avoid downloading or sharing the material. Consult a qualified legal professional if you need advice about a specific situation.
How to Stay Safe Online When You Encounter AIO-TLP371
You do not need to interact with an unverified download to understand a trending topic. In many cases, reading reliable reporting and following basic security practices is enough to answer your questions.
The following steps can help protect your computer, phone, accounts, and personal information.
1. Research the source before trusting it
Start by looking for information about the website and the specific claim. Search for independent reporting, official security advisories, and statements from relevant organizations.
Avoid treating copied blog posts as independent confirmation. If several pages repeat exactly the same claim without identifying an original source, they may all be relying on the same unverified information.
Check whether the evidence supports the precise claim being made. A report confirming that a company experienced a breach does not necessarily confirm that a particular file package contains authentic data from that incident.
2. Keep your operating system and applications updated
Security updates often fix vulnerabilities that attackers may exploit. An outdated browser, operating system, document reader, or archive utility may be more susceptible to known attacks.
Enable automatic updates where practical, and install applications through official stores or verified publisher websites.
Updates cannot eliminate every threat, but they reduce exposure to vulnerabilities for which fixes are available.
3. Use reputable security software
Keep the built-in security features of your operating system enabled or use a reputable security product that meets your needs.
If a downloaded file triggers a warning, do not ignore it just because a webpage describes the file as safe. Stop and investigate the warning through the security product’s official documentation.
You should not disable antivirus protection to open a file from an unknown source. A page that insists you must turn off security controls is a strong reason to leave.
4. Avoid installing unknown extensions
Browser extensions can sometimes read or modify information on websites you visit. The permissions granted to an extension determine what it may be able to access.
Install extensions only when you have a clear reason to use them. Check the publisher, reviews, permissions, and official listing before installation.
If an unfamiliar website asks you to install an extension to access an alleged leak, consider that request unnecessary unless a trustworthy, independently verified explanation establishes otherwise.
5. Protect important accounts with multifactor authentication
Multifactor authentication adds another verification step beyond a password. Depending on the service, this might involve an authenticator app, a security key, or another supported method.
It is especially useful for email, financial services, cloud storage, and accounts used to reset other passwords.
Use unique passwords alongside multifactor authentication. Neither measure guarantees complete protection, but together they can make unauthorized account access more difficult.
6. Review browser permissions
If a website unexpectedly asks to send notifications, access your location, use your camera, or access your microphone, ask whether that permission is necessary.
For ordinary informational pages, many of these permissions are unnecessary.
You can review and revoke website permissions through your browser settings. The exact menu names differ between browsers, but the relevant controls are generally found in privacy, security, or site-permission settings.
7. Scan suspicious files carefully
If you have already received a suspicious file, avoid opening it. You can consult your security software or a trusted security professional about how to assess it.
Online file-scanning services may help identify known malicious files, but they have limitations. A clean result is not proof that a file is harmless, particularly if the threat is new or the file requires execution to reveal its behavior.
Also consider privacy before uploading a file to an online scanner. The service may retain or share submitted samples with security researchers or participating organizations. Do not upload confidential documents, private photographs, credentials, or sensitive business records without understanding the service’s handling practices.
8. Know what to do if you already downloaded something
If you downloaded a file associated with an unverified leak, do not panic. The appropriate response depends on what you downloaded and whether you opened or executed it.
Start with these steps:
- Do not open or run the file if you have not already done so.
- Remove the file if it is unwanted and your security software has not advised a different containment procedure.
- Run a security scan using a reputable product.
- If you executed the file and suspect compromise, disconnect the affected device from the network when appropriate and seek trusted technical assistance.
- From a separate, trusted device, change potentially exposed passwords and review account sessions.
- Contact your organization’s IT or security team if the affected device contains workplace data.
If you notice unauthorized transactions, contact your bank using its official contact details. If sensitive work information may have been exposed, follow your organization’s reporting procedures.
The important lesson is to respond methodically rather than following additional instructions from the suspicious website.
TheJavaSea.me Down: What Does It Mean?
People sometimes search phrases such as “thejavasea.me down” when they cannot open a website. A failed connection can have several explanations, and it does not automatically mean that a site has been shut down permanently.
Common reasons a website may be unavailable
- Temporary server problems: The hosting service may be experiencing an outage.
- DNS issues: The domain name may not be resolving correctly.
- Network restrictions: A network provider, workplace, school, or security filter may block access.
- Domain changes: The domain may have expired or its configuration may have changed.
- Maintenance: The operator may have temporarily disabled some or all of the site.
- Security action: A hosting provider or another relevant authority may have restricted a service.
These are general explanations, not verified findings about thejavasea.me’s current status.
Should you search for mirror websites?
Be careful. When a website becomes unavailable, copycat domains may appear and claim to provide the same content. Some may be unrelated, while others may use the original name to attract visitors.
A mirror is not automatically authentic or safe. Do not install certificates, browser extensions, or applications simply because a supposed replacement site tells you to.
If your goal is to learn about the AIO-TLP371 keyword, reading credible sources is safer than searching for unofficial copies of an unverified file collection.
How can you check availability safely?
For ordinary troubleshooting, use reputable domain-information services or general website-status tools. Remember that a status checker only reports limited technical information. It cannot establish whether a website’s content is genuine, lawful, or safe to download.
There is no need to visit a suspicious mirror simply to determine why a domain is unavailable.
TheJavaSea.me Alternatives: Safer and Legal Options
People searching for “thejavasea.me alternatives” may have different goals. Some want information about an alleged leak, while others are looking for software, educational resources, documents, or general technical information.
The safest alternative depends on what you actually need. Instead of searching for another site offering the same unverified files, start with the original purpose of your search.
1. Official software websites
If you are looking for an application, obtain it directly from its developer or an authorized distributor.
Official sources are more likely to provide current releases, documentation, licensing details, and legitimate update mechanisms. They also make it easier to identify the publisher responsible for the software.
Before installing anything, verify the publisher and make sure the download matches your device and operating system.
2. Authorized digital marketplaces
If you need a paid application, game, creative tool, or productivity resource, consider an authorized marketplace.
These platforms often provide licensing information, compatibility details, customer support, and an established process for updates. Availability and pricing vary, but legitimate distribution reduces the uncertainty associated with anonymous archives.
3. Open-source repositories
When your goal is to find open-source software or developer tools, use recognized project repositories and the project’s official documentation.
Check the project’s maintainers, license, release history, and installation instructions. A repository’s public availability does not automatically make every uploaded file trustworthy, so verify the project and publisher before running code.
4. Free and open educational resources
If you are searching for learning materials, look for resources released by educational institutions, libraries, public agencies, and recognized learning platforms.
Many provide free articles, textbooks, lectures, tutorials, and research materials without requiring users to obtain unauthorized copies.
These sources can be useful alternatives when the original search involves documents or technical information rather than a particular application.
5. Public cybersecurity advisories
If your main interest is understanding whether a leak is genuine, consult reputable cybersecurity organizations and official incident announcements.
Such reports can explain what is known, what remains uncertain, and what affected users should do. They may also identify protective measures without exposing readers to the underlying files.
A credible report should distinguish confirmed findings from allegations and avoid presenting speculation as fact.
6. Contact the original publisher or data owner
If the material is supposed to come from a company, service, or individual, seek information through their official communication channels.
For software, this may mean checking the publisher’s documentation or support pages. For a suspected personal-data breach, it may mean looking for a verified incident notice and following its recommended steps.
This approach is particularly important when the material could include private or confidential information.
How to Evaluate a Website Before Downloading Anything
A simple evaluation process can help you make better decisions about unfamiliar websites, including those mentioned in searches for thejavasea.me leaks aio-tlp371.
| Check | What to look for | What it tells you |
|---|---|---|
| Source identity | A clear, verifiable operator | Who appears responsible for the website |
| Independent evidence | Reliable reporting or official statements | Whether important claims have support |
| File provenance | A verified publisher and documented source | Whether the file’s origin is reasonably established |
| Security warnings | Alerts from reputable security tools | Whether known risks have been detected |
| Permissions | Requests that match the site’s purpose | Whether access requests appear necessary |
| Privacy policy | Clear information about data handling | How the service says it manages personal information |
| Licensing | Permission to distribute the material | Whether the intended use may be authorized |
No single check can guarantee safety. A website can provide a privacy policy and still behave deceptively, while a legitimate small project may have limited documentation.
Use several indicators together, and pay attention to inconsistencies. If the claims are extraordinary but the evidence is weak, it is sensible to stop rather than take unnecessary risks.
What Should Website Owners and Publishers Learn From Leak-Related Searches?
The topic also has lessons for publishers, website administrators, and organizations responsible for sensitive data.
Make security information easy to find
Organizations should provide clear guidance about official software downloads, security advisories, incident reporting, and support contacts. When trustworthy information is difficult to find, users may rely on unofficial sources.
A clear official page can help visitors distinguish legitimate releases from misleading copies.
Respond to suspected leaks carefully
If an organization learns that confidential information may have been exposed, it should investigate before making public claims. Relevant steps may include preserving evidence, assessing the scope of the incident, containing unauthorized access, and notifying affected people where required.
Organizations should avoid publishing sensitive details that could make the incident worse. Communications should clearly distinguish confirmed facts from ongoing investigations.
Respect the privacy of affected people
A leaked file may include information about people who have no connection to the website where it appears. Republishing that information can cause further harm.
Publishers covering alleged leaks should consider whether a detail is necessary for public understanding and whether it can be discussed without reproducing private material.
Avoid misleading SEO claims
A website should not claim that a particular archive is authentic, verified, or safe unless it has credible evidence supporting that description.
Clear language about uncertainty helps readers understand what is known and prevents speculation from being presented as fact. It also builds trust more effectively than sensational headlines.
Frequently Asked Questions About theJavaSea.me Leaks AIO-TLP371
1. What is thejavasea.me leaks aio-tlp371?
It is a search phrase associated with thejavasea.me and an identifier called AIO-TLP371. The exact meaning, contents, and authenticity of the alleged material have not been established here, so it should be treated as an unverified topic.
2. Is thejavasea.me safe?
Its safety cannot be determined from the domain name alone. Avoid downloading unknown files, entering sensitive information, or installing software from a source you have not independently verified.
3. Is AIO-TLP371 a legitimate software package?
There is not enough verified information here to establish that AIO-TLP371 is a legitimate software package or to confirm what it contains. A label or online claim is not proof of authenticity.
4. Can files from leak websites contain malware?
Yes. Files from unverified sources can contain malware, deceptive installers, or links to phishing pages. Not every file is malicious, but a file’s advertised name and description do not prove that it is safe.
5. What should I do if I downloaded a suspicious file?
Avoid opening it if you have not already done so, and scan your device with reputable security software. If you ran the file and suspect a compromise, seek trusted technical assistance and secure potentially affected accounts from a separate, trusted device.
6. What are safe alternatives to thejavasea.me?
The appropriate alternative depends on what you need. Use official software publishers, authorized marketplaces, recognized open-source repositories, educational libraries, or reputable cybersecurity advisories instead of relying on unverified leak archives.
Conclusion
The keyword thejavasea.me leaks aio-tlp371 raises questions about a website, an unfamiliar identifier, and alleged leaked material. However, the keyword itself does not establish what the files contain, whether a leak is authentic, or whether the website is safe.
The most useful response is to approach the topic with care. Verify claims through independent sources, avoid suspicious downloads, protect your accounts, and respect the privacy and legal rights of people whose information may be involved.
If your goal is to find legitimate software or reliable information, official publishers and reputable educational or cybersecurity resources provide a clearer starting point. You can investigate a trending topic without putting your device, accounts, or personal information at unnecessary risk.
The general rule is straightforward: verify the source before trusting the claim, and never treat an unfamiliar download as safe simply because it is popular online.
About the Author